Kenya Cyber Security Directive 2026: Critical PHP Vulnerabilities, Enterprise Web Application Patching & Incident Response

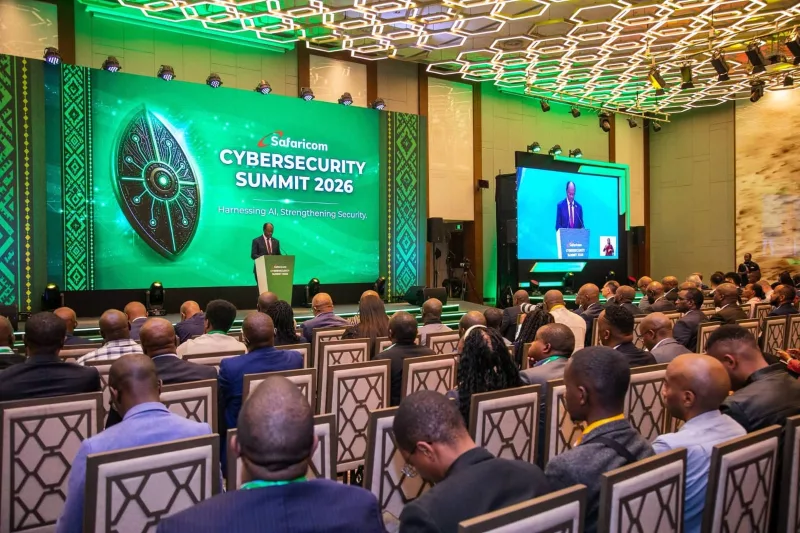
nformation, Communications and the Digital Economy Cabinet Secretary William Kabogo speaking during the Safaricom Cyber Security Summit 2026./HANDOUTAccess Services
The government has issued an urgent cybersecurity advisory directing public institutions to identify and address critical vulnerabilities affecting websites and web applications powered by PHP. The warning places renewed attention on enterprise web application security, vulnerability management and the protection of digital public services against potential remote code execution attacks.
The advisory, issued on October 21, 2026, by the State Department for ICT and the Digital Economy in collaboration with the ICT Authority, concerns two PHP vulnerabilities rated 9.2 on the Common Vulnerability Scoring System (CVSS). According to reporting on the directive, successful exploitation could allow attackers to execute malicious code on affected servers, potentially exposing sensitive information and disrupting online services.
Read Also: Pharmacy Board Looks to Shape Future of Pharmaceutical Practice
The directive prioritises internet-facing government websites, application servers and other systems running vulnerable PHP versions. It also requires institutions to assess third-party applications, hosting platforms and managed services that may contain affected components. Where immediate remediation is not possible, agencies have been advised to consider restricting external access or temporarily taking affected services offline until appropriate protections are implemented.
Expert commentary — enterprise cybersecurity and systems auditing
“An emergency vulnerability advisory should trigger a coordinated response involving system administrators, security teams, application owners and external service providers. Organisations need to identify exposed assets, verify the correct software fixes, test deployments and preserve evidence of suspicious activity. A patching exercise is only complete when the organisation has confirmed that the vulnerable component has been addressed and the affected system is operating securely.”
Critical PHP Vulnerabilities and the Risk to Government Portals
PHP is widely used to build dynamic websites, content management systems, application interfaces and online service portals. Its widespread adoption means a vulnerability in the underlying runtime can affect systems across different sectors, particularly where organisations operate outdated software or lack visibility into their hosting environments.
The October advisory identifies two critical flaws reported as CVE-2026-109618 and CVE-2026-109619, associated with the threat described as “php2shell”. Both were reported with CVSS scores of 9.2. Administrators should verify the identifiers, affected versions and applicable fixes against the official PHP security announcements and relevant vendor advisories before deploying updates.
Remote code execution is especially serious because it can allow an attacker to run commands or malicious code on a vulnerable server. The consequences depend on the server’s permissions, network configuration and access to other systems. Potential risks include unauthorised access to application data, exposure of credentials, modification of website files and disruption of public services.
A vulnerable website does not automatically mean that a successful attack has occurred. Nevertheless, the severity of the reported flaws warrants immediate investigation, especially where applications are accessible from the public internet.
Government agencies should begin by compiling an inventory of PHP installations, including those operated by contractors and third-party hosting providers. The assessment should cover production servers, test environments, legacy applications and services that may have been deployed without complete documentation.
Mandatory Patching Windows and Vulnerability Remediation
The advisory calls on institutions to prepare for and apply the relevant security updates promptly once the correct fixes have been verified. However, the available reporting does not establish a universal numerical deadline, such as six, 12 or 24 hours, for patching every affected system. Organisations should not publish an invented deadline as an official government requirement.
The appropriate response is to prioritise remediation according to exposure, severity and operational risk. Public-facing systems containing sensitive information or supporting essential services should receive immediate attention.
System administrators should identify the PHP version running on each affected server and establish whether it contains the vulnerable component. The team should then confirm the correct patched release, test the update where practical and deploy it through an approved change-management process.
Updating a website’s theme or plugin alone may not resolve a vulnerability in the underlying PHP runtime. Administrators must verify that the actual runtime and relevant server processes are using a fixed version.
Read Also: KNEC Grade 10 Assessment 2026: Guidelines, Timelines & School Requirements
Where immediate patching is impossible, the advisory recommends considering restrictions on external access or temporarily taking the affected service offline. Such decisions should be coordinated with service owners to reduce disruption while maintaining security.
Temporary web application firewall rules and access controls can reduce exposure during remediation. However, these measures should supplement, not replace, the installation of the appropriate security updates.
Enterprise Web Application Security and Third-Party Providers
The directive also highlights a challenge facing institutions that outsource website development, cloud hosting or application maintenance. An organisation may depend on a supplier to manage its technical infrastructure, but it still needs sufficient information to understand the security risks affecting its services.
ICT departments should contact software developers, managed service providers and hosting companies to establish whether their systems use vulnerable PHP components. Contracts and service-level agreements should be reviewed to determine who is responsible for applying patches, investigating incidents and communicating security risks.
Enterprises should also assess whether vulnerable applications share credentials, databases or network access with other services. Isolating systems and limiting privileges can reduce the potential impact if an attacker compromises one application.
A useful security review should cover access permissions, administrative accounts, backup arrangements, application dependencies and the ability to restore services following an incident. These controls are particularly important for portals that process personal information, payments or confidential institutional records.
Cybersecurity Incident Reporting and NC4 Timelines
Patching is only one part of the response. Institutions must also determine whether the vulnerability has been exploited and whether suspicious activity requires formal incident reporting.
The National Cyber Incident Reporting Hub provides a reporting route for individuals, private organisations, government institutions and entities responsible for critical information infrastructure. The hub advises organisations to contain active incidents, preserve evidence, classify the impact and submit reports through the appropriate channel.
Kenya’s Computer Misuse and Cybercrimes Act, 2018 includes a reporting obligation under Section 40 concerning attacks, intrusions and other disruptions to computer systems or networks. The statutory provision establishes a 24-hour reporting period for the specified incidents. This is an incident-reporting requirement, not a universal 24-hour software-patching deadline. Organisations should verify the statutory wording and reporting route applicable to their circumstances.
Additional obligations may apply to designated critical information infrastructure and regulated businesses. The Communications Authority of Kenya’s National KE-CIRT/CC coordinates national cybersecurity incident response and publishes relevant technical advisories.
Institutions should therefore distinguish three separate activities: fixing a vulnerability, reporting a suspected or confirmed incident and complying with any sector-specific notification requirements. A vulnerability alert alone does not establish that a breach has occurred, but evidence of exploitation should trigger the appropriate investigation and reporting process.
Technical Threat Metrics and Remediation Windows
| Technical Threat Metric | Affected Web System | Mandatory Remediation Window |
|---|---|---|
| CVSS 9.2 — critical severity | Internet-facing government websites running vulnerable PHP versions | Prompt remediation following verification of the appropriate security updates; no universal numerical patching deadline confirmed in the available advisory reporting. |
| Remote code execution risk | PHP-powered web applications and application servers | Prioritise immediate assessment and patching according to exposure and operational risk. |
| Vulnerable runtime or dependency | Third-party applications, hosting platforms and managed services using affected PHP components | Establish affected versions and coordinate remediation with the relevant service provider without delay. |
| Suspected exploitation or unauthorised access | Application, server, endpoint and network infrastructure | Investigate immediately, preserve evidence and report through the appropriate cybersecurity channel where required. |
| System cannot be secured promptly | Exposed websites and web applications that remain vulnerable | Consider restricting external access or temporarily taking the service offline until effective mitigation is implemented. |
| Confirmed reportable cyber incident | Government, enterprise or designated critical infrastructure systems | Apply the relevant statutory and sector-specific reporting deadline; the general Section 40 reporting provision specifies 24 hours for the incidents it covers. |
The table distinguishes the urgency of the technical response from a legally prescribed deadline. Agencies should follow the original advisory and any subsequent official instructions when determining exact implementation schedules.
Incident Response Frameworks and Evidence Preservation
Organisations should activate their incident response procedures whenever monitoring identifies suspicious activity that may be connected to an affected application. The initial investigation should establish the systems involved, the period of potential exposure and whether unauthorised access or changes to application files have occurred.
The advisory recommends reviewing web server, application, endpoint and network logs for unusual requests, unexpected file modifications, unauthorised access attempts and suspicious processes. Security teams should preserve relevant evidence before performing actions that could erase important forensic information.
Where compromise is suspected, the response should include containment, assessment of the potential impact, removal of malicious components and recovery from trusted systems or backups where necessary. Credentials and access tokens should be reviewed if there is evidence that they may have been exposed.
Institutions should also record the actions taken, the systems assessed, the versions updated and any remaining risks. Clear documentation allows management to establish whether remediation is complete and provides evidence for subsequent audits.
The National KE-CIRT/CC offers a national coordination point for cybersecurity information and incident response. Organisations should use the appropriate reporting channel and comply with any additional obligations applying to their sector.
What ICT Directors and Enterprise Leaders Should Do
The directive makes asset visibility and clear accountability essential. ICT directors should ensure that every public-facing application has an identified technical owner and that the organisation can establish which software components support its services.
Security teams should prioritise vulnerable internet-facing systems, coordinate with suppliers and verify the successful deployment of updates. Where remediation is delayed, the organisation should document the reason, apply compensating controls and establish a clear plan for resolving the exposure.
Senior management should also ensure that cybersecurity risks are reflected in business continuity planning. Taking a public portal offline may interrupt service delivery, but leaving a critical vulnerability exposed can create a more serious operational and reputational risk.
Regular vulnerability assessments, tested backups, controlled administrative access and a documented incident response framework can improve readiness for future security advisories. These measures should form part of routine technology governance rather than being activated only after an emergency announcement.
Read Also: Top Comoros Official Hospitalized in Nairobi Amid Rising Tensions in Moroni
Protecting Kenya’s Digital Public Services
Kenya’s October 2026 PHP security advisory underscores the importance of maintaining secure software across government portals and enterprise web applications. The reported CVSS 9.2 vulnerabilities create an urgent need to identify affected systems, apply verified fixes and investigate signs of potential exploitation.
The response must extend beyond installing updates. Institutions need to assess third-party infrastructure, preserve evidence, review access controls and follow the applicable cybersecurity incident-reporting requirements.