Kenya AI Bill 2026: High-Risk Systems Face New Oversight as Data Protection Rules Take Centre Stage

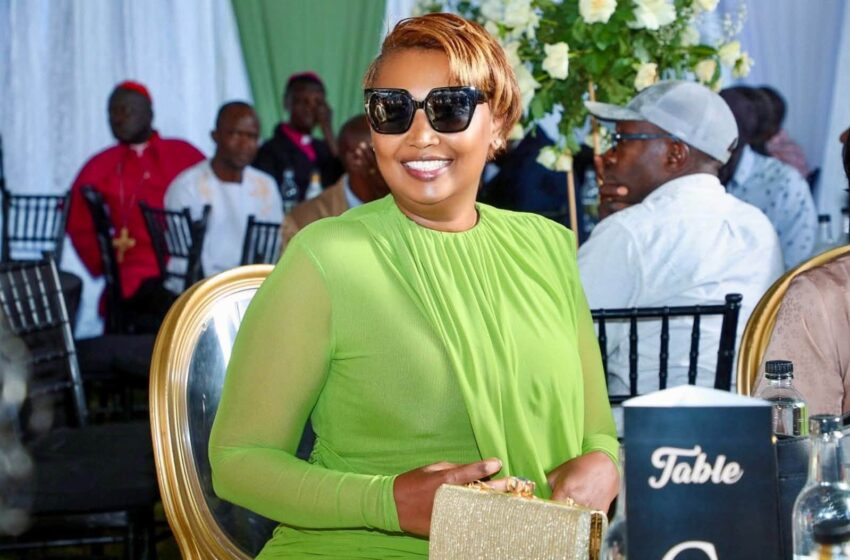
minated Senator Karen Nyamu, who is sponsoring the Artificial Intelligence Bill, 2026. IMAGE/ Courtesy
The proposed Artificial Intelligence Bill, 2026 could introduce a new layer of oversight for businesses, public institutions and technology developers deploying artificial intelligence, placing risk assessments, transparency and data protection at the centre of the country’s digital governance framework.
The legislation proposes establishing an Office of the Artificial Intelligence Commissioner, classifying AI systems according to risk and introducing specific obligations for providers and deployers of high-risk technologies. The measures could affect organisations using automated decision-making in areas such as finance, healthcare, education, recruitment and public service delivery.
The Bill is before the legislative process and should not be treated as an enacted law. Its provisions may change as Parliament considers the proposal. Nevertheless, the text offers businesses an indication of the governance requirements that could emerge as AI adoption expands across Kenya.
Read Also: Pharmacy Board Looks to Shape Future of Pharmaceutical Practice
The official Bill published by Parliament sets out a proposed framework covering risk classification, impact assessments, transparency, cybersecurity and accountability. These provisions would operate alongside existing laws, particularly the Data Protection Act, 2019, which already governs the processing of personal data.
Proposed Office of the AI Commissioner
A central feature of the Bill is the proposed establishment of an Office of the Artificial Intelligence Commissioner to oversee the regulation and governance of AI systems.
Under the proposed framework, the Commissioner would have responsibilities that include overseeing compliance, issuing guidance, supporting risk management and maintaining a public register of high-risk AI systems. The Bill also provides for an advisory structure intended to support the governance framework.
The proposed office would create a dedicated institutional focus for AI-related risks rather than leaving every issue to regulators whose existing mandates cover different aspects of technology, privacy and consumer protection.
For businesses, a specialised regulator could provide clearer guidance on the responsibilities attached to developing, supplying or deploying AI systems. Public institutions could also face closer scrutiny when adopting automated technologies for decisions affecting citizens.
However, the relationship between the proposed office and existing authorities would be important. The Office of the Data Protection Commissioner (ODPC), for example, already has responsibilities under Kenya’s data protection legislation. Any new AI governance framework would need to operate alongside those powers without creating uncertainty over enforcement.
The Senate’s committee report on the Artificial Intelligence Bill provides further context on the legislative process and the issues considered by lawmakers.
High-risk AI systems and proposed compliance duties
The Bill proposes a risk-based approach, recognising that not all AI applications present the same potential harm.
A system used to recommend entertainment content does not necessarily carry the same risks as one used to assess a loan application, evaluate a job applicant or influence access to essential public services. Systems capable of affecting rights, livelihoods or access to important services may require more extensive safeguards.
Under Section 26 of the published Bill, providers and deployers of high-risk AI systems would be required to conduct risk assessments before deployment and introduce measures to reduce identified risks, including human oversight.
The proposed requirements also include human rights impact assessments, transparency and traceability, cybersecurity safeguards, and records covering data inputs, training datasets, system outputs and performance metrics for at least five years.
These obligations would place greater emphasis on documenting how an AI system operates and demonstrating that risks have been considered before the technology is introduced.
Organisations using AI to support recruitment, credit scoring, medical decisions or public administration would need to identify the consequences of system errors, discriminatory outcomes and inappropriate reliance on automated recommendations.
The Bill also proposes a public register of high-risk AI systems. Such a register could help improve visibility into the technologies used by public institutions and other organisations, although its practical operation would depend on the final law and implementing regulations.
Businesses should not assume that every AI tool automatically falls into the high-risk category. The applicable classification and requirements would need to be assessed against the final statutory framework and any guidance issued by the relevant authority.
Data Protection Impact Assessments and the ODPC
Data Protection Impact Assessments (DPIAs) are likely to remain a central compliance issue for organisations using AI to process personal information.
A DPIA is a structured assessment of how a proposed data-processing activity may affect individuals’ privacy and rights. It helps organisations identify risks before processing begins and determine what safeguards are necessary.
Kenya’s existing Data Protection Act, 2019 already provides for DPIAs where processing is likely to result in a high risk to the rights and freedoms of individuals. The ODPC has also published guidance on data protection impact assessments.
Read Also: KNEC Grade 10 Assessment 2026: Guidelines, Timelines & School Requirements
The proposed AI Bill would add AI-specific obligations for high-risk systems, including compliance with the Data Protection Act and DPIAs where required. This distinction matters: the Bill should not be described as having already introduced a universal DPIA requirement for every AI deployment.
A lender using an automated model to evaluate customers, for instance, may need to consider the type of personal data involved, the consequences of inaccurate decisions, the possibility of unfair discrimination and the mechanisms available for individuals to challenge outcomes.
A hospital using AI to support patient assessment would need to consider confidentiality, the sensitivity of health information, access controls and the potential consequences of incorrect recommendations.
The ODPC’s existing enforcement powers remain relevant where organisations breach data protection requirements. The proposed AI framework would not remove the need to comply with current privacy law while Parliament considers the new legislation.
Data hosting, localisation and cloud infrastructure
The growth of AI has renewed debate about where personal information is stored, where it is processed and which organisations can access it.
Many Kenyan businesses rely on cloud infrastructure supplied by international technology companies. AI applications may also transmit information to third-party platforms for analysis, storage or model processing. These arrangements can raise questions about security, international transfers and accountability.
However, the proposed AI Bill should not be interpreted as imposing a blanket requirement for all AI data to be hosted in Kenya.
Existing Kenyan law provides specific rules for certain categories of personal data and cross-border transfers. The Data Protection Act and related regulations establish conditions under which personal data may be transferred outside the country. Additional localisation requirements can apply to prescribed personal data associated with strategic or state interests.
The ODPC’s public-sector guidance explains requirements concerning data localisation and transfers for relevant public-sector processing.
Organisations should therefore identify the legal basis for each hosting and transfer arrangement rather than assuming that every dataset must remain within Kenya’s borders.
A company using an overseas cloud provider should understand where information is stored, who processes it, what contractual protections apply and whether the proposed transfer meets Kenya’s legal requirements.
Penalties and enforcement: What organisations should understand
Regulatory consequences are another concern for businesses preparing for tighter oversight of automated technologies.
The ODPC already has enforcement powers under the Data Protection Act, including the ability to investigate complaints and impose administrative penalties in accordance with the law. Organisations that unlawfully process personal information cannot rely on the fact that an AI system made the decision as a defence against their responsibilities as data controllers or processors.
The proposed AI Bill sets out a separate governance framework, including obligations for high-risk systems and provisions addressing offences and penalties. The exact consequences applicable to a particular breach must be assessed against the Bill’s text and its eventual final form.
Businesses should avoid treating proposed penalties as though they are already enforceable under a law that has not completed the legislative process.
The distinction is especially important for fintech firms, telecommunications operators, healthcare providers and companies handling large volumes of customer information. Their existing obligations under privacy, consumer protection and sector-specific laws continue to apply regardless of the Bill’s status.
Organisations should also ensure that responsibility for AI decisions is clearly assigned. Outsourcing a system to a vendor does not necessarily remove a company’s obligations concerning the personal data it controls or processes.
What fintech and telecommunications companies should do now
Financial technology and telecommunications businesses are among the organisations that could face complex compliance questions as AI adoption grows.
Fintech firms may use automated tools to detect fraud, assess creditworthiness, identify suspicious transactions and personalise financial products. Telecommunications operators may deploy AI for customer support, network management, identity verification and fraud prevention.
Some applications may involve sensitive information, extensive profiling or decisions with significant consequences for individuals. Companies should examine these uses individually instead of applying the same controls to every AI tool.
Practical preparation can begin before the proposed Bill becomes law.
Organisations should maintain an inventory of AI systems, identify whether personal data is involved, document the purpose of each application and establish who is responsible for monitoring its performance.
They should also review whether DPIAs are required under existing law, assess vendors’ security practices, verify cross-border transfer arrangements and establish procedures for responding to complaints or correcting harmful outcomes.
Where AI supports decisions affecting customers, businesses should consider how staff can review questionable results and how affected individuals can seek clarification or challenge decisions.
These measures can help organisations improve accountability under the current legal framework while preparing for possible additional requirements.
Balancing innovation with accountability
Kenya’s proposed AI Bill arrives as businesses and public institutions explore ways to use automation to improve efficiency, expand services and analyse large amounts of information.
Clear governance rules could help establish expectations for responsible deployment and strengthen public confidence in AI-assisted services. However, compliance costs, uncertainty over classification and the capacity of regulators will influence how effectively the framework operates.
Smaller technology firms may face particular challenges if assessments, documentation and technical safeguards require resources they do not readily have. Guidance, proportionate implementation and regulatory clarity could therefore become important considerations as the Bill progresses.
The legislation also raises questions about how Kenya can encourage local AI development while protecting individuals from discrimination, privacy violations and decisions that cannot be adequately explained.
The proposed Office of the AI Commissioner, high-risk system obligations and interaction with existing data protection rules are central to that debate.
Read Also: Top Comoros Official Hospitalized in Nairobi Amid Rising Tensions in Moroni
For businesses, the immediate priority is to distinguish proposed obligations from existing legal duties. The Bill is not yet a substitute for the Data Protection Act, and organisations must continue meeting current requirements governing personal data, DPIAs where necessary and lawful cross-border transfers.
If enacted in its current or a revised form, the legislation could give Kenya a more specialised framework for AI governance. Its ultimate effect will depend on the final text, implementing guidance, enforcement arrangements and the ability of businesses to translate legal requirements into practical safeguards.